Cybersecurity
Security Architecture
SERVICE ENGINEERING GUIDE
Design security around how people, devices and applications actually interact. We define trust boundaries, enforcement points and operational ownership before products are installed, giving implementation teams a coherent blueprint.
What we deliver in practice
Trust boundaries & segmentation
Map users, workloads and data into security zones. Define permitted connections and administrative paths; identify enforcement points for campus, data centre, cloud and third-party access.
Zone model and application communication matrix.
Identity-led access
Design authentication and authorisation around user role, device posture and resource sensitivity. Separate privileged administration from ordinary access and define exception and emergency-access procedures.
Identity patterns and privileged-access design.
Protection & detection layers
Position network, endpoint, application and data controls around the threat model. Define log sources, meaningful detections and response ownership so controls can be operated after deployment.
Control architecture and telemetry coverage map.
Migration & design assurance
Review compatibility, capacity and failure modes. Plan phased enforcement, rollback and design-review gates; translate principles into buildable configuration requirements and acceptance scenarios.
HLD/LLD, decision register and transition plan.
The technology, explained
Zero trust
Access is evaluated for the requested resource using identity and context rather than assumed safe because of network location. It is an approach spanning people, process and technology.
NAC / 802.1X
Network access control uses identity and device context to decide access. 802.1X is a port-based authentication mechanism; exceptions require deliberate policy.
SIEM / EDR
SIEM correlates security telemetry; EDR focuses on endpoint detection and response. Both require configured coverage, tuned detections and accountable responders.
Reference architectures & design practices
Illustrative patterns for project discussions. Final topology, sizing, products and acceptance criteria are developed against your requirements. These are BrightGate concept diagrams, not vendor-certified designs.
Identity-aware access to segmented applications+
On smaller screens, scroll the diagram sideways to see all components.
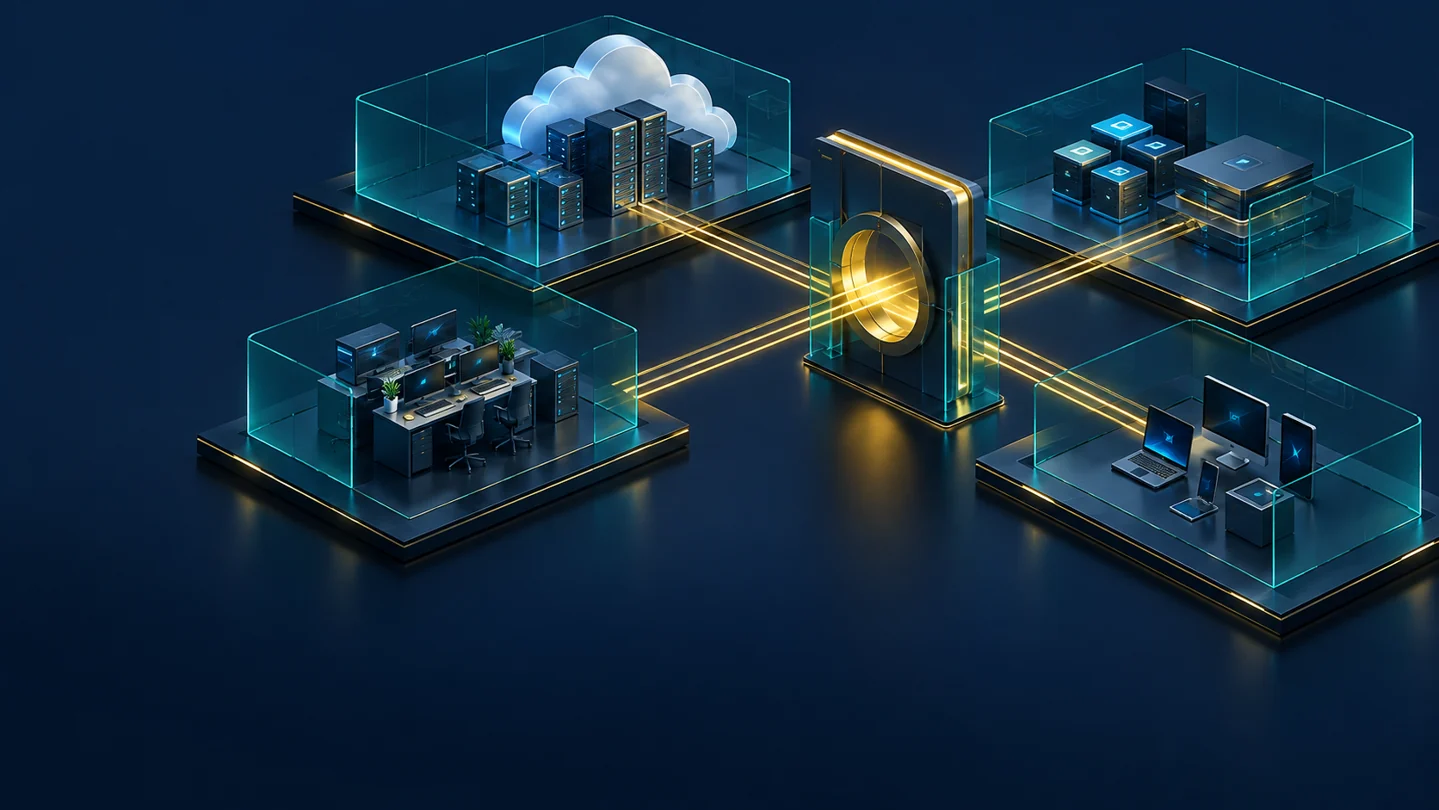
Identity and device context inform a policy decision before access to a protected resource. Application and data zones limit permitted paths, while telemetry supports review. Zero trust is an architectural approach, not a product switch or a promise that breaches cannot occur.
Design practices to apply
- Enforce least privilege at meaningful boundaries.
- Separate policy decisions from logging-only visibility.
- Design failure behaviour for identity dependencies.
Systems, products & official references
Examples to evaluate during scoping. Selection, supported features, hardware and licences depend on the agreed solution; a product mention does not imply a certification or an included purchase.
Zero-trust design principles
A reference for resource-focused access and policy enforcement.
Official reference NIST Zero Trust ArchitectureNGFW / NAC / identity controls
Product families selected around enforcement location and integration requirements.
Official reference Fortinet FortiGate firewallsSIEM / EDR / privileged access
Detection, endpoint response and administrative controls are designed as complementary capabilities.
A result your team can accept
Acceptance evidence
Design coverage
Trace priority threats and application flows to proposed controls.
Feasibility
Review compatibility, capacity and ownership with implementers.
Enforcement
Specify allowed/blocked tests and failure-mode expectations before build.
View the complete capability checklist
- Zero-trust and identity-centred access design
- Network microsegmentation and trust boundaries
- Secure hybrid-cloud and remote-access architecture
- IAM, PAM and multi-factor authentication design
- Endpoint, email and data-protection architecture
- SIEM, SOC and detection-engineering architecture
- Resilience, recovery and security control integration
- Threat scenarios, design reviews and control traceability